
Chatter watch identified chatter increasing on X (ARTEX is a U.S. trend; about 2,085 posts in 33 minutes, and about 9,260 in 2.5 hours) after FBI Dallas posted the Bureau’s November 13 FLASH advisory.
Quick take
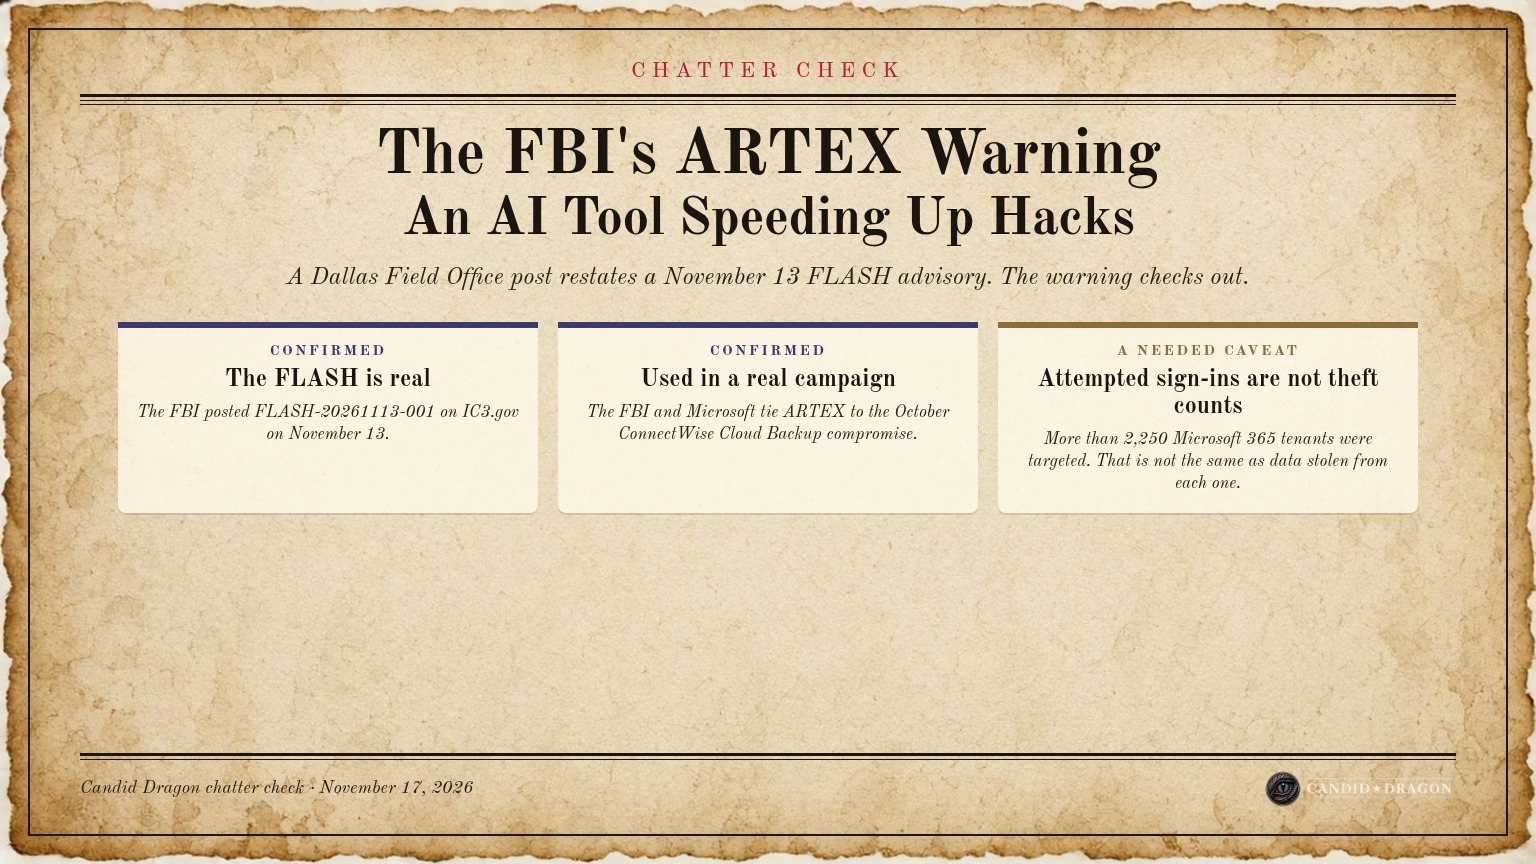
- The FBI Dallas post is real. It summarizes an official FBI FLASH, FLASH-20261113-001, issued November 13 and posted on IC3.gov.
- The FLASH says criminals and state-aligned actors have used ARTEX, an open-source AI-agent penetration testing framework, since at least August 2026, and that some intrusions went from initial targeting to privileged access in under three hours.
- The FBI and Microsoft say ARTEX was used in the October ConnectWise Cloud Backup supply-chain compromise, with attempted sign-ins to more than 2,250 downstream Microsoft 365 tenants. A sign-in attempt is not the same as confirmed data theft at every tenant. ConnectWise has said it cannot see into those tenants well enough to confirm that count.
- This is a real warning about faster, automated intrusions. It is not evidence of a global internet shutdown, wiped bank balances, or a single coordinated attack behind today’s outages.
Our rating: ✅ Confirmed  Factual
Last updated November 17, 2026, 1:40 p.m. CT.
✅ Confirmed Factual Lean note: The Dallas Field Office post accurately restates the FBI’s November 13 FLASH, which is posted on IC3.gov. Microsoft’s October investigation and ConnectWise’s own advisories support the ConnectWise campaign. The main caveat is scope: attempted authentication is not confirmed data theft at all 2,250-plus tenants.
What the post said, and what checks out
At 9:01 a.m. CT on November 17, the official FBI Dallas account posted that the FBI had issued a FLASH advisory warning that cybercriminals and state-aligned hackers are exploiting ARTEX, which it called a “super intelligence-powered penetration testing framework,” to automate attacks against businesses and organizations worldwide. The post said ARTEX can accelerate intrusions from initial targeting to privileged access in under three hours, and that it was used in the October ConnectWise supply-chain compromise, “which exposed Microsoft 365 customer environments and involved attempted authentication against more than 2,250 downstream tenants.” It urged organizations to strengthen access controls, monitor suspicious automated activity, and report potential compromises to ic3.gov, and linked to the advisory at ic3.gov/CSA/2026/261113.pdf.
That link is a real FBI product: FLASH-20261113-001, “Threat Overview of ARTEX Autonomous Penetration Testing Framework,” dated November 13, 2026, and marked TLP:CLEAR, meaning it may be shared without restriction. The advisory says ARTEX is an open-source, large-language-model-driven agentic platform that threat actors have weaponized to automate multiple phases of intrusions, from reconnaissance through data theft, “at machine speed.” It says a variety of malicious cyber actors have used it since at least August 2026 against organizations in financial services, government, technology, defense, semiconductors, energy, healthcare, manufacturing, telecommunications and the legal industry. It also says some intrusions progressed from initial targeting to privileged access in under three hours.
The FLASH’s own wording for the tool is “specialized super intelligence (SI) agents.” In plain language, these are AI agents that can carry out many steps of an intrusion with little human help after someone sets the goal. The FBI says ARTEX does not include its own model and instead hooks up to outside AI services.
The advisory is not new today. It was issued on November 13. Security outlets including BleepingComputer (November 15) and TechCrunch (November 16) had already reported it. What is new this morning is the Dallas Field Office post, which by early afternoon had been viewed about 2.9 million times. ARTEX was a U.S. trend on X as of 1:33 p.m. CT. An X search for posts about the ARTEX FLASH counted about 2,085 posts between 1:00 and 1:33 p.m. CT, and about 9,260 from 11:00 a.m. to 1:33 p.m. CT. As of this writing, we did not find a matching public advisory from CISA.
The ConnectWise campaign
On this point, the Dallas post is mostly precise and slightly loose in one phrase. The FLASH describes “a supply chain compromise affecting ConnectWise Cloud Backup customers that resulted in attempted sign-ins to more than 2,250 downstream tenants.” That matches Microsoft’s October 21 investigation, which attributed the campaign to a China-state-aligned actor it tracks as Storm-0940 and said the actor used ARTEX to attempt to sign in to more than 2,250 tenants after compromising application identities used by ConnectWise Cloud Backup, formerly SkyKick Cloud Backup. Microsoft also reported that, in several ARTEX-driven attacks, the time from initial targeting to privileged access was less than three hours.
The looser wording is “exposed Microsoft 365 customer environments.” Microsoft was careful to say that a successful sign-in, or the presence of an affected application, does not necessarily mean customer data was accessed or stolen. ConnectWise, in its Trust Center advisories, confirmed unauthorized access to Cloud Backup application credentials, first disclosed on October 16, and later said a China-state-aligned group used “an openly available agentic AI framework” to automate and speed up the operation. A ConnectWise spokesperson told TechCrunch the company does not have the visibility to confirm the 2,250-tenant figure cited by the FBI. Huntress, which investigated affected Microsoft 365 tenants in October, reported at least 162 compromised tenants at the time.
The FLASH also cites financially motivated attacks against South Korean financial institutions that led to the theft of personal information from about 67,000 people. That is a separate campaign described in the same advisory, not part of the ConnectWise incident.
What this is not
The warning is circulating on the same day as a scheduled one-minute Emergency Alert System test and a cluster of unrelated outage rumors. The FLASH is a real FBI product about a real tool used in real campaigns. It is not evidence that the internet is being shut down, that bank balances are being wiped, or that today’s Apple and NSA disruptions are part of one coordinated attack. Those are separate claims, and we have covered them in our November 17 rumor check and our Apple and NSA outages check.
What small businesses should do
The FBI is not asking the public to take emergency action. It is asking organizations to harden ordinary defenses and to watch for automated activity that moves faster than a typical break-in. For a small business, the practical steps are straightforward:
- Tighten access controls. Review who, and which third-party apps, can reach your email, files and backups. Remove unused app permissions. Give people and tools only the access they need, especially for Microsoft 365, cloud admin pages and backup platforms.
- Turn on multi-factor authentication for email, financial accounts and any administrator login, and prefer an authenticator app or a security key over text-message codes where you can.
- Watch for automated activity. Look for bursts of failed or unusual sign-ins, new apps you did not approve, unexpected administrator accounts, and sudden changes to privileges or credentials. The FBI notes that ARTEX-driven attacks can be “noisy,” but they can also finish before a person has time to respond.
- If you or your IT provider uses ConnectWise Cloud Backup (formerly SkyKick), follow ConnectWise’s current Trust Center guidance, keep affected connections disabled until you are told otherwise, and review sign-in and audit logs in each Microsoft 365 tenant. Microsoft’s investigation has a hunting and review section for that incident.
- Report suspected compromises to the FBI’s Internet Crime Complaint Center at ic3.gov, or to your local FBI field office. Be wary of emails or texts that use this warning as bait to “fix” your account or sell you a tool.
Sources
- FBI, FLASH-20261113-001, “Threat Overview of ARTEX Autonomous Penetration Testing Framework,” November 13, 2026, posted on IC3.gov
- FBI Dallas, post on X, November 17, 2026, 9:01 a.m. CT
- Microsoft Security Blog, “AI-driven, large-scale nation-state campaign using ARTEX enables supply chain compromise,” October 21, 2026
- ConnectWise Trust Center, Cloud Backup (formerly SkyKick) advisories, first published October 16, 2026, including the October 21 attacker update
- ConnectWise, Cloud Backup technical investigation and remediation guide
- Huntress, “ConnectWise (SkyKick) Vendor Credentials Abused in M365 Attacks”
- Lawrence Abrams, BleepingComputer, “FBI warns ARTEX AI hacking tool is powering global cyberattacks,” November 15, 2026
- Zack Whittaker, TechCrunch, “FBI says Artex AI open source hacking tool used to breach networks in ‘under three hours,’” November 16, 2026
- The Record, “FBI flash alert says Artex tool automating cyberattacks at ‘machine speed’”
Featured image: Candid Dragon almanac graphic, November 17, 2026. See all image credits.