

Chatter watch identified chatter increasing on X (about 377 posts in an hour) after JPMorgan Chase said third-party vendors were hit by a cyberattack.
Quick take
- New: Reuters reviewed leaked files posted by the group calling itself n0n and says they appear to show 124 bank employee emails and more than 16,000 Chase customer emails, some with phone numbers or postal codes, plus Visa Asia-Pacific and Mastercard marketing data. Reuters could not independently verify the authenticity of the data. Those contents remain ❓ Unconfirmed.
- New: Visa and Mastercard confirmed that limited cardholder data was exposed through the same vendor attack. Both say no card numbers were taken and that their own networks were not affected.
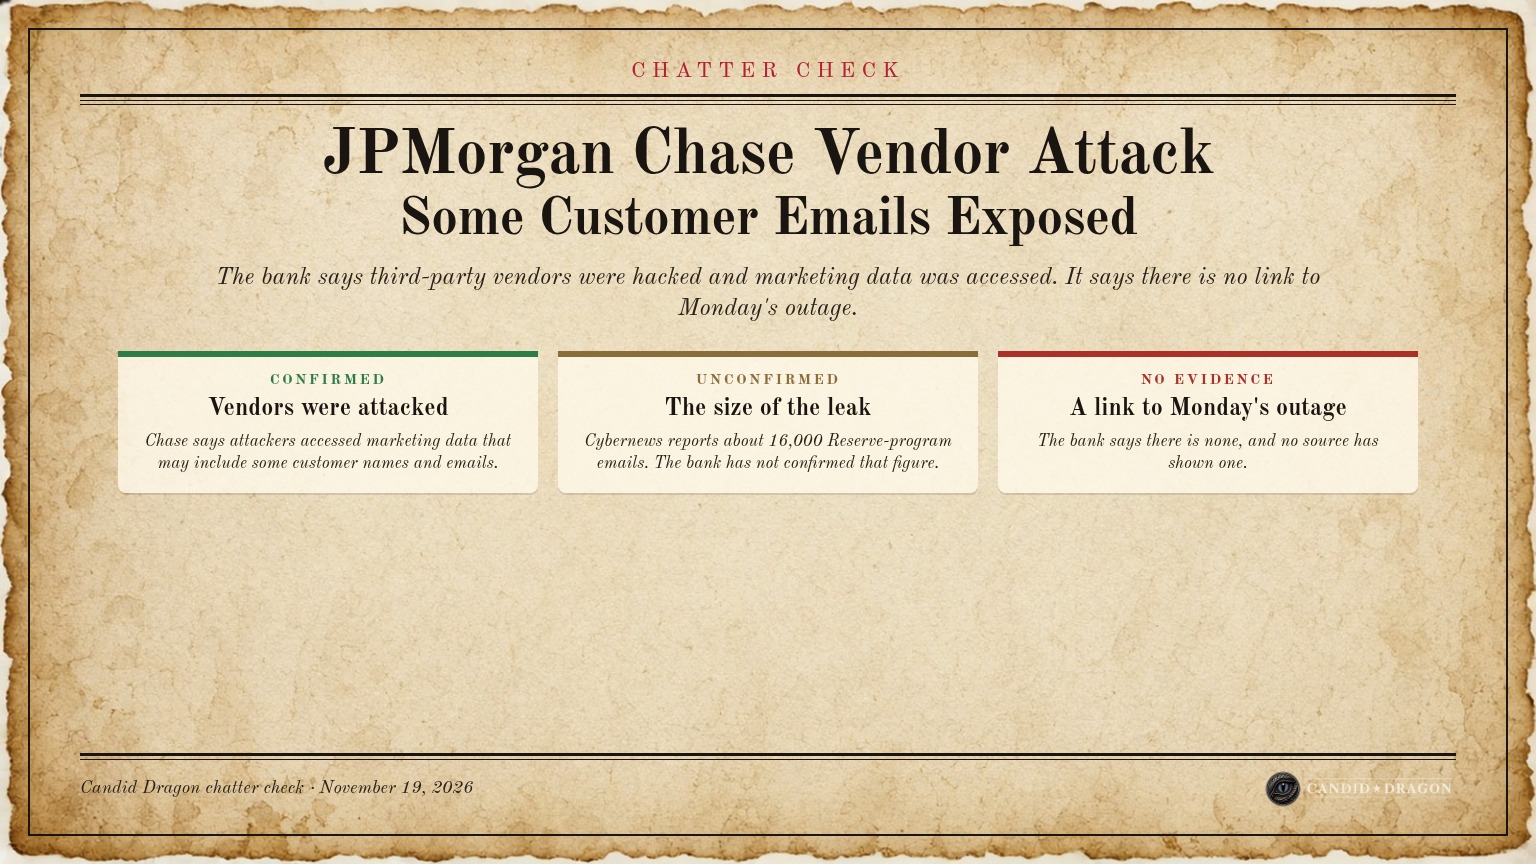
- JPMorgan Chase says third-party vendors that serve the bank were hit by a cyberattack.
- Attackers accessed marketing data that may include some customer names and email addresses, the bank says.
- The bank says its services were not disrupted and it will contact affected customers and offer credit monitoring.
- JPMorgan says this has no connection to Monday’s outage, which it blamed on a software bug.
- A cyber outlet reports about 16,000 JPMorgan Reserve emails, about 6,000 premium Visa customers and about 2,000 Mastercard customers; none of the companies has confirmed those counts. Those figures are ❓ Unconfirmed.
Our rating: ✅ Confirmed  Factual
Last updated November 19, 2026, 12:20 p.m. CT.
✅ Confirmed Factual Verdict: A confirmed vendor breach, not proof the week’s outages were an attack. Chase, Visa and Mastercard have all confirmed that limited customer data was exposed through third-party vendors. The leak contents and counts reported by Cybernews, and reviewed by Reuters, remain Unconfirmed. Reuters said it could not independently verify the authenticity of the data. A link to Monday’s outage is not supported — the companies describe a data incident, not a payment-network or banking outage, and no source has shown a connection.
What we know
In a statement posted on X at 7:17 a.m. CT Thursday, JPMorgan Chase (Factual) said “third parties who provide services to the firm were the target of a cyber attack.” “Based on our investigation so far, we believe the attackers accessed certain marketing data held by those vendors, which may include some customer names and email addresses,” the bank said. “There is no disruption to our services.” The same wording was reported by ABC News (Factual) and Reuters (Factual).
The bank did not name the vendors or say when the attack happened. It said that, where appropriate, it will contact affected customers and offer complimentary credit monitoring. It also said it found “no connection to service disruption some customers experienced earlier this week.” ABC News and Reuters both reported that Chase blamed Monday’s outage on a software bug. Reuters, citing unnamed sources, also reported that the Treasury Department and the Office of the Comptroller of the Currency called banks after Monday’s outage to check that it was contained and was not a cyber incident.
Visa and Mastercard. Visa and Mastercard also confirmed that limited cardholder data was exposed in a third-party vendor attack. Bloomberg (Factual), via Moneycontrol, reported that Visa said the incident was tied to a third-party company in Asia, that Visa’s own systems were not involved, and that payment data such as card numbers were not affected. Mastercard said a “limited amount of non-payments information from a subset of cardholders enrolled in a specific benefit program” was exposed and that there was no impact to its network. Mastercard spokesperson Seth Eisen told The Verge (Factual) that the breach exposed “a limited amount of email addresses” belonging to a “small subset of cardholders enrolled in a specific benefit program.” Visa’s statement that payment data such as card numbers were not affected was also reported by The Verge, citing Visa’s comments to Cybernews.
Unconfirmed leak details. Cybernews (Factual) reported that a gang calling itself n0n published leaks that its researchers say include about 16,000 customer email addresses tied to JPMorgan’s invitation-only Reserve card program, datasets connected to about 6,000 premium Visa customers, and about 2,000 Mastercard customers, “if authentic.” None of the companies has confirmed those counts, the Reserve-program link, or the gang’s involvement. Those figures remain Unconfirmed. Reuters (Factual), in a review of files posted by the group, said the data appears to include 124 bank employee email addresses and more than 16,000 customer email addresses, some with phone numbers and postal codes. Reuters said the Visa files appear focused on Asia-Pacific markets and include thousands of purported customer emails, phone numbers and marketing-campaign data, and that the Mastercard files include marketing data related to customers in North America, the Middle East and Africa, plus a small number of Mastercard employee emails. Reuters could not independently verify the authenticity of the data. JPMorgan declined to comment on the data.
The confirmed fact is the vendor breach itself. It is not evidence that this week’s wave of outages was a coordinated attack. Those are separate claims, and the outage-as-attack claim remains Disputed. See also our November 16 bank-outage chatter check.
On X, posts about the Chase vendor attack rose quickly Thursday morning, from a few dozen an hour to about 377 posts in the 9 a.m. CT hour, then about 455 posts in the 10 a.m. CT hour. Posts about a Visa or Mastercard breach rose from about 20 an hour to about 248 in an hour. Some replies to the bank’s statement called the timing “not a coincidence.” Volume on the broader outage-as-attack claim also rose earlier, to about 72 posts an hour from 38. No official or researcher has produced evidence tying the vendor breach to Monday’s outage.
What to watch
- The names of the vendors and when the attack happened — the bank has not said.
- Whether the bank confirms the n0n leak or the roughly 16,000-email figure, and when affected customers are notified.
- The name of the vendor or vendors — Visa pointed to a third-party company in Asia, but none of the firms has named it — and any statement from regulators.
Latest updates
🔄 November 19, 2026, 12:20 p.m. CT: Reuters reviewed data posted by the group calling itself n0n and says it appears to include 124 bank employee email addresses and more than 16,000 customer email addresses, some with phone numbers and postal codes. In Reuters’ review, the Visa files appear focused on Asia-Pacific markets and include thousands of purported customer emails, phone numbers and marketing-campaign data; the Mastercard files include marketing data related to customers in North America, the Middle East and Africa, and a small number of Mastercard employee emails. Reuters could not independently verify the authenticity of the data, and JPMorgan declined to comment on it (Reuters, via Investing.com). Those leak contents and counts remain Unconfirmed. Rating unchanged.
🔄 November 19, 2026, 11:00 a.m. CT: Visa and Mastercard confirmed that limited cardholder data was exposed in the same vendor attack. Visa said the incident was tied to a third-party company in Asia, that Visa’s own systems were not involved, and that there is no indication payment data such as card numbers were affected (The Verge; Bloomberg, via Moneycontrol). Mastercard said a limited amount of non-payments information from a subset of cardholders enrolled in a specific benefit program was exposed, with no impact on its network; spokesperson Seth Eisen told The Verge that meant “a limited amount of email addresses.” Cybernews reports datasets tied to about 16,000 JPMorgan Reserve customers, about 6,000 premium Visa customers and about 2,000 Mastercard customers, “if authentic”; no company has confirmed those counts, which remain Unconfirmed. Posts about the Chase vendor attack rose to about 455 in the 10 a.m. CT hour. Posts about a Visa or Mastercard breach rose from about 20 an hour to about 248 in an hour. Rating unchanged.
🔄 November 19, 2026, 10:15 a.m. CT: First published. We will update this page if the bank names the vendors, confirms the size of the leak, or if a regulator comments.
Label key
- ✅ Confirmed An official record, or two or more independent outlets, agree.
- ❓ Unconfirmed Reported or claimed, but not yet independently verified.
- ⚠️ Disputed Contradicted by the evidence or by credible sources, or actively contested.
- Factual Straight reporting that holds up across outlets on different sides.
 Leans Left The facts hold, but the coverage tilts left: one-sided, loaded language, missing context or a single anonymous source.
 Leans Right The facts hold, but the coverage tilts right: one-sided, loaded language, missing context or a single anonymous source.
 Likely Propaganda State-run or state-aligned media, a militant press office, a partisan campaign or group, or unverifiable spin.
Each story gets one confidence tag and one source-lean label, plus a one-line Lean note explaining the call. Every side is held to the same standard. More on how we cover the news.
Sources
- Nupur Anand and AJ Vicens, Reuters, “JPMorgan, Visa, Mastercard say third-party vendors targeted in cyberattack,” November 19, 2026, via Investing.com
- Emma Roth, The Verge, “JPMorgan Chase reveals data breach, but says it’s unrelated to this week’s banking outage,” November 19, 2026
- Bloomberg, “Visa, Mastercard, JPMorgan disclose customer data exposure in third-party vendor cyberattack,” November 19, 2026, via Moneycontrol
- JPMorgan Chase, statement on X, November 19, 2026, 7:17 a.m. CT
- Bill Hutchinson, ABC News, “JPMorganChase reports cyberattack on third-party service providers,” November 19, 2026
- Reuters, “JPMorgan says third-party vendors targeted in cyberattack,” November 19, 2026, via StreetInsider
- Gintaras Radauskas, Cybernews, “Hacker leaks details of JPMorgan’s ultra-wealthy cardholders,” November 19, 2026
- Candid Dragon, “Apple and NSA outages: is the week’s wave of failures an attack? Chatter check”
- Candid Dragon, “U.S. bank outages, November 16 chatter check”
- X post counts (search and count tools), November 19, 2026
Featured image: Candid Dragon almanac graphic, November 19, 2026. See all image credits.
Get Ready List
This chatter check is about a confirmed vendor cyberattack, not a blackout. The outage-and-cyber rule still points to cash, a radio and spare batteries as baseline gear.
 GOOD TO HAVE
Cash, a weather radio and spare batteries
Why. The rule for outages and cyber is cash, radio and batteries. A vendor data breach is not by itself a power or payments outage, so this stays at baseline, not a rush. (This chatter check.)
Buy before the rush: Hand-crank emergency radio with flashlight (Coming soon — Candid Dragon store link). Keep a few days of cash in small bills (not a store item); see what to have on hand when banks or card payments go down. A power bank or portable power station (Coming soon — Candid Dragon store link)
This is a preparedness recommendation, not a claim that the whole country has run out. Ratings follow the Get Ready List key on PrepperCast. Orders are not open yet.